Claims clear faster with the same headcount, fewer are paid in error, and you can tell the regulator and your customers that health data stays on company systems alone.
Back to Private LLM
Insurers · 12 / 12
Private LLM for claims and underwriting
Claim documents, medical records and application forms read on the insurer’s own systems and summarised for faster decisions, with customers’ health data going nowhere.
 Insurers
“One claim comes with a medical certificate, receipts and ten pages of treatment notes, and a person reads every one. We want AI to help, and it is customers’ health data, so it cannot go outside.”
The problem
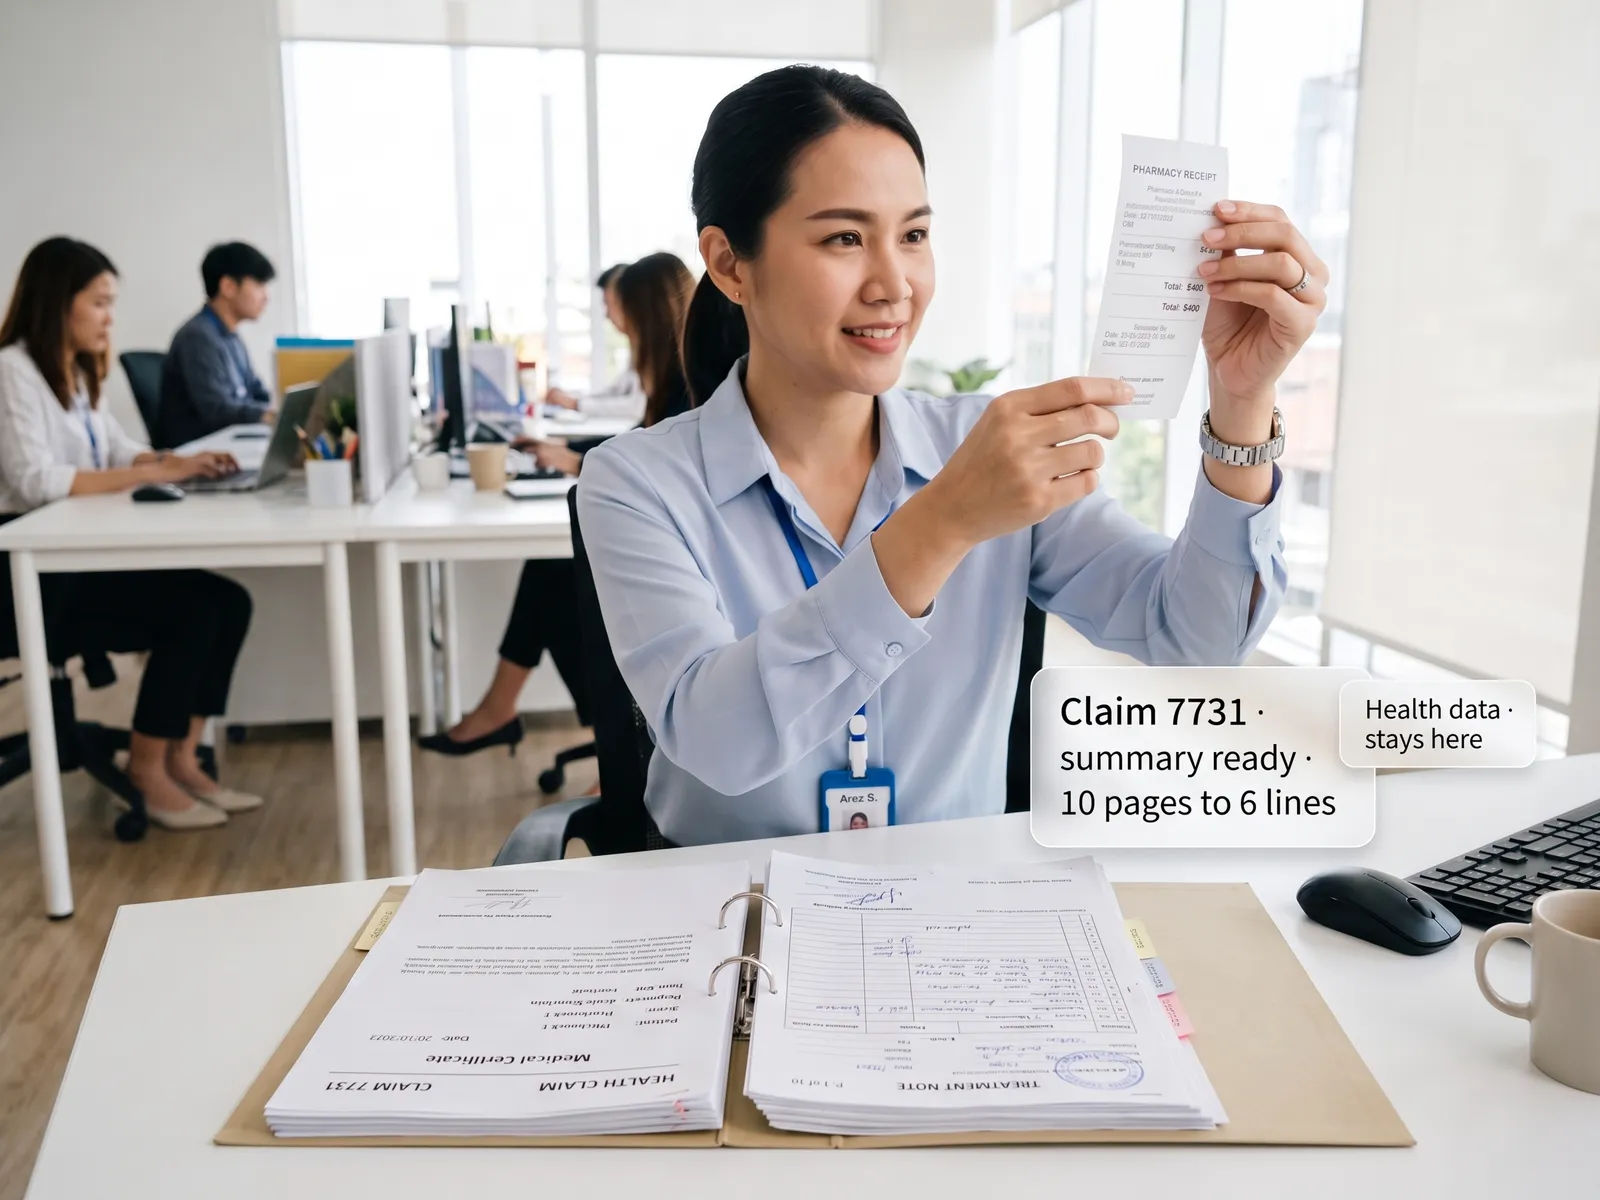
One health claim arrives with a medical certificate, several receipts and treatment notes scanned as images. The claims assessor reads all of it, compares it with the policy terms and types a summary before approval. In a busy period the backlog runs to weeks and customers phone every day to ask whether their claim has come up. Underwriting reads application forms and health check results the same way.
Every document holds health data, which is sensitive personal data under PDPA and sits under the insurance regulator. It cannot go to an outside tool to read. So the team keeps reading.
How we solve it
We install a language model on the company’s own servers or in a cloud account the company controls and connect it to the claims and policy systems you already run. When a claim comes in, the system reads every page, scanned images included, summarises on one page what was treated and for how much, compares it with that policy’s cover, and flags which items fall outside the terms and which documents are still missing.
For underwriting, the system summarises the medical history from the application and test results, with the points worth asking the doctor about. Permissions follow the role, so health data is visible only to the person responsible for that case. Every view goes into an audit log for the DPO and compliance. There are no external API calls.
The system summarises and flags. Approving or declining a claim, and accepting or declining a risk, remain decisions for the authorised officer. Anything the system flags as irregular always goes to the investigation team for a person to look at first.
How it runs
Work comes in from
- Claim documents from LINE OA and branches
- Application forms and health check results
- Policy terms in the system
- Past claims history
What the AI does
- Read the documents, scanned images included
- Compare with the cover
- Summarise and flag what needs checking
- Log every access
Where it lands
- One-page summary to the claims assessor
- Summary to the underwriter
- Irregular cases to the investigation team
- Audit log for the DPO and compliance
Before and after
Before
After
Assessors read ten pages per claim; in peak season the backlog runs to weeks
A one-page summary with the items outside cover is ready before the assessor opens the case
Customers phone every day to ask whether their claim has come up
A claim with complete documents is decided the same day
An irregular claim is found after it has been paid
The system flags patterns resembling past cases for the investigation team before payment
What you get
- 01
A model inside the company’s systems that reads scanned medical certificates, receipts and treatment notes and summarises the claim on one page
- 02
Claim items compared with the policy terms and benefit table, with items outside cover and missing documents flagged
- 03
An underwriting assistant that summarises the medical history from the application and test results, with the points to ask the doctor about
- 04
Claims that resemble past cases found to be irregular flagged and passed to the investigation team for a person to look at first
- 05
Role-based permissions, so health data is visible only to the person handling that case, with an audit log on every access under PDPA
Who gets what
Installed on your infrastructure, connected to the claims and policy systems read-only at first, permissions from Active Directory, an audit log on every access, and designed with the DPO.
Assessors stop reading receipts one at a time and typing the summary themselves, and get the time for the cases that actually need judgement.
Who this fits
Life insurersHealth insurersGeneral insurersLarge insurance brokersThird-party claims administrators (TPAs)
Connects with what you already run
Core InsuranceClaims SystemMicrosoft 365Active DirectoryLINE OASharePoint
Development process
- 1
Discover
Requirements, users and success metrics, with scope and price fixed before we start.
- 2
Design
UX and system architecture; the prototype is approved before anything is built.
- 3
Build
AI-accelerated sprints with a demo every week, reviewed by senior engineers.
- 4
Test
QA, security and performance verified against the agreed scope.
- 5
Launch & care
Production deploy, team training, and a monthly care plan.
Turn your business problem into a system that works for you
Tell us today — get an executive-ready proposal with the plan and budget.
Talk to an engineer about thisMore solutions in Private LLM
See the whole service Legal & contracts Private LLM for contract work HR teams HR assistant on a Private LLM Finance & accounting Private LLM for financial documents R&D & engineering Private LLM for engineering knowledge Customer service teams Customer reply assistant on a Private LLM Executives & the board Private LLM for executives and the board Banks & financial institutions Private LLM for financial institutions Hospitals Private LLM for health data Law firms & consultancies Private LLM for clients’ confidential documents Telecoms & ISPs Private LLM for telecom operators Energy & utilities Private LLM for critical infrastructure